PAYLOAD Group Weaponizes Windows Group Policy to Take Down an Entire Domain Without Touching a Single File
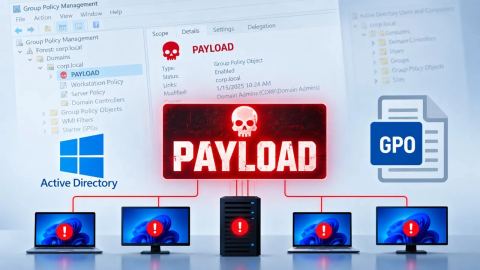
A ransomware crew calling itself PAYLOAD breached a Middle Eastern manufacturer's Windows domain and disrupted it enterprise-wide using nothing but malicious Group Policy Objects — no encryption, no malware binaries, and almost nothing for traditional antivirus to catch. The post PAYLOAD Group Weaponizes Windows Group Policy to Take Down an Entire Domain Without Touching a Single File appeared first on Secure Bulletin.
Itagora tiene in archivio titolo e sommario per la ricerca interna. Il testo completo resta sulla fonte. Il link in uscita non invia referrer.