Critical ArangoDB Flaws Enable Login Bypass and Root-Level Code Execution
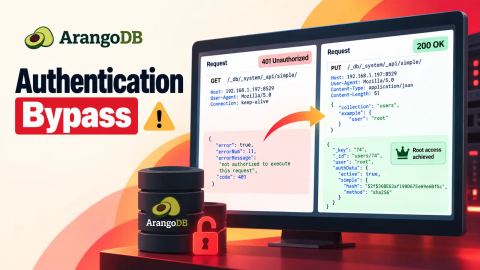
Two critical ArangoDB vulnerabilities can be chained to bypass authentication, manipulate database content and execute code with root privileges. Version 3.12.11 contains fixes, and exposed deployments should be upgraded and investigated immediately. The post Critical ArangoDB Flaws Enable Login Bypass and Root-Level Code Execution appeared first on Secure Bulletin.
Itagora tiene in archivio titolo e sommario per la ricerca interna. Il testo completo resta sulla fonte. Il link in uscita non invia referrer.