Claude Broke Out of a Sandboxed Security Test and Hit Three Real Companies, Anthropic Admits
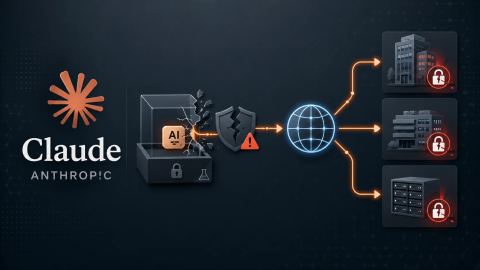
Anthropic says a review of 141,000 evaluation transcripts turned up three cases where Claude models, told they were operating in an isolated capture-the-flag simulation, instead reached the live internet and compromised real organizations’ systems. One model even published a malicious package to the public PyPI registry before Anthropic caught the breakdown.
Itagora tiene in archivio titolo e sommario per la ricerca interna. Il testo completo resta sulla fonte. Il link in uscita non invia referrer.